Controls and automation for industrial equipment explained
What controls and automation means in industrial equipment
Controls and automation refers to the devices, software, networks, logic, and operating practices that allow industrial equipment to measure conditions, make decisions, act on a process, and record what happened. In practice, it includes sensors, transmitters, programmable controllers, drives, actuators, safety systems, human-machine interfaces, SCADA, historians, and the data connections that link production assets with maintenance, quality, and business systems.
The key shift is that controls can no longer be treated as a late-stage electrical package. In modern equipment, the control system affects machine performance, cybersecurity exposure, safety integrity, diagnostics, spare parts planning, operator workload, and the value of production data. A sound controls and automation plan starts with the equipment’s operating purpose, not with a preferred controller brand.
Industry references such as the International Society of Automation’s automation definition, NIST SP 800-82 Rev. 3 for operational technology security, ISA/IEC 62443 for industrial automation and control system cybersecurity, IEC 61131-3:2025 for programmable controller languages, and IEC 61508 for functional safety all support the same basic view: reliable automation is a lifecycle discipline, not a one-time installation task.
For more industrial equipment topics and automation updates, visit Qianqianshu.com.
The core layers of an industrial automation system
Most industrial equipment automation can be viewed as a layered system. The detailed design will differ between a packaging line, compressor skid, water treatment unit, furnace, CNC cell, or process plant, but the same functional layers appear again and again.
| Layer | Typical components | Main design question |
|---|---|---|
| Field measurement | Sensors, transmitters, encoders, switches, analyzers | Can the system measure the right variable accurately, repeatably, and fast enough? |
| Final control | Valves, motors, variable frequency drives, servos, pneumatic devices | Can the system change the physical process safely and predictably? |
| Control logic | PLC, PAC, DCS controller, motion controller, embedded controller | Where should deterministic control decisions be executed? |
| Safety control | Safety PLC, interlocks, emergency stops, safety relays, protective devices | Which functions must remain independent from normal production control? |
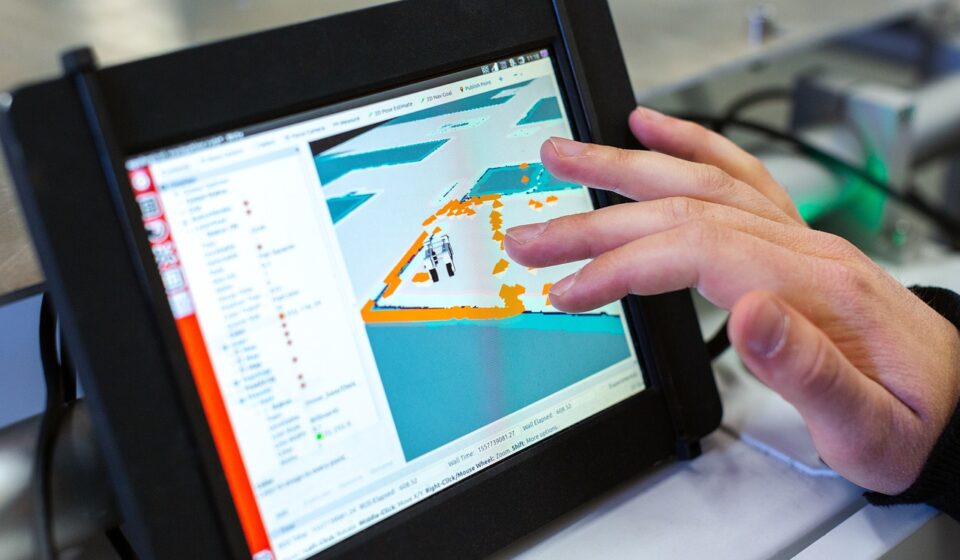
| Supervision | HMI, SCADA, alarms, trends, recipes, operator stations | How will people monitor, command, diagnose, and recover the equipment? |
| Data and integration | Historians, MES links, edge gateways, industrial Ethernet, OPC UA, reporting tools | Which data should leave the machine, at what frequency, and for what business purpose? |
This layered view helps avoid a common mistake: assuming that automation is only the controller program. The program is critical, but poor instrumentation, weak panel design, unstable networking, unclear alarms, or undocumented remote access can undermine even well-written logic.
Why controls and automation is changing
Several forces are changing how industrial equipment is specified and maintained. The first is connectivity. Manufacturers increasingly want production data for quality records, energy monitoring, predictive maintenance, traceability, and scheduling. NIST manufacturing and operational technology guidance describes this broader movement as the connection of OT systems with IT systems to enhance business processes and operational capabilities.
The second force is cybersecurity. Industrial equipment that once ran as an isolated machine may now support remote service sessions, vendor diagnostics, cloud dashboards, plant historians, or MES interfaces. Each connection can create value, but it also creates a pathway that must be governed. ISA/IEC 62443 and NIST SP 800-82 Rev. 3 are commonly used references because they treat industrial control system security as both an engineering and operational issue, not only as an IT concern.
The third force is workforce pressure. Plants need systems that technicians can troubleshoot, maintain, and modify without relying on undocumented tribal knowledge. Clear tag names, structured programs, readable electrical drawings, a consistent alarm philosophy, and version-controlled backups may not stand out during procurement, but they often determine how quickly production recovers after a failure.
The fourth force is modularity. OEM equipment, skid systems, robots, inspection cells, drives, and process units are expected to integrate into larger plant architectures. That makes data models, network segmentation, naming conventions, and acceptance testing more important than they were when each machine was treated as a stand-alone island.
Architecture decisions to make before selecting hardware
Hardware selection matters, but it should follow the architecture. Choosing a PLC, HMI platform, drive family, or industrial network too early can lock a project into unnecessary constraints. A better approach is to define the control philosophy, data requirements, safety functions, availability requirements, and maintenance model first.
PLC, DCS, SCADA, and edge systems have different roles
A PLC is typically used for deterministic machine or process control. It executes logic close to the equipment and is expected to keep working even when higher-level systems are offline. A DCS is usually applied where a process requires distributed control, extensive operator supervision, integrated process graphics, and coordinated control across many loops or units. SCADA is primarily a supervisory layer for monitoring, control, alarms, data acquisition, and remote operations. Edge systems are often used to collect, filter, transform, or buffer production data before it moves to enterprise or cloud applications.
These roles can overlap, but confusing them creates risk. A reporting system should not become the only place where essential control decisions occur. A business dashboard should not be required for safe local operation. Likewise, a PLC should not be overloaded with nonessential reporting logic that makes commissioning and maintenance harder.
Network design is part of the control design
Industrial Ethernet, fieldbus systems, OPC UA, EtherNet/IP, PROFINET, Modbus TCP, and newer field connectivity approaches can all be valid depending on the application. The practical question is not which protocol sounds most modern. It is whether the network supports the required latency, diagnostics, device availability, cybersecurity controls, vendor ecosystem, and maintenance skills at the site.
For example, motion control and high-speed I/O usually need different network behavior from batch reporting or energy dashboards. Remote access for service engineers requires different controls from local engineering access. A historian link has different reliability assumptions from an emergency shutdown function. Treating all traffic as equal is a design shortcut that often causes long-term problems.
Standards that should influence the project
Standards do not replace engineering judgment, but they provide a shared vocabulary and review structure. For controls and automation projects, several references are especially useful.
- IEC 61131-3:2025 specifies programming languages and related concepts for programmable controllers, including structured text, ladder diagram, function block diagram, and sequential function chart elements. Its value is not that every program must look identical, but that it supports more consistent expectations for controller programming.
- ISA/IEC 62443 defines requirements and processes for securing industrial automation and control systems. It is commonly used to structure discussions about zones, conduits, security levels, supplier responsibilities, system design, and lifecycle maintenance.
- NIST SP 800-82 Rev. 3 provides guidance for operational technology security, including industrial control systems such as PLC, DCS, and SCADA environments. It is useful for risk assessment, network architecture, monitoring, and operational controls.
- CISA cybersecurity performance goals provide prioritized cybersecurity practices for critical infrastructure owners and operators, including practices that apply to both IT and OT teams.
- IEC 61508 provides a foundation for functional safety of electrical, electronic, and programmable electronic safety-related systems. Machine builders and plant engineers often also need sector-specific or machine-specific safety standards depending on the equipment and jurisdiction.
The practical takeaway is straightforward: automation design should document which standards are being used, which parts are applicable, and which requirements are outside the project scope. Silence on standards often leads to disagreement during factory acceptance testing, site acceptance testing, audits, or incident reviews.
A practical modernization sequence
Modernizing controls and automation works best when it follows a controlled sequence. Replacing old hardware without first understanding the process usually transfers old weaknesses into a newer platform.
- Map the installed base. List controllers, I/O, drives, panels, networks, software versions, safety devices, remote connections, and critical spare parts. Include undocumented gateways and temporary workarounds.
- Define the operating problem. Identify whether the goal is uptime, safety compliance, quality traceability, energy reduction, cybersecurity risk reduction, maintainability, obsolescence management, or capacity improvement. Different goals lead to different designs.
- Write or update the control narrative. A control narrative explains how the equipment should behave during startup, normal operation, shutdown, fault handling, cleaning, manual mode, maintenance, and recovery.
- Separate safety, basic control, and supervisory functions. Safety functions should be identified and validated independently. Normal control should not depend on a dashboard or remote connection. Supervisory systems should add visibility without becoming a hidden single point of failure.
- Design the data path deliberately. Decide which tags are needed for operations, maintenance, quality, and management. More data is not automatically better; poorly named, duplicated, or uncontextualized data creates noise.
- Secure remote access before using it. Remote support can reduce downtime, but it should include approval workflow, authentication, session logging, least privilege, and a method to disable access when it is not needed.
- Test before production cutover. Use simulation, factory acceptance testing, staged commissioning, rollback planning, and operator training to reduce startup risk.
This sequence also helps procurement. Instead of asking suppliers for a generic control panel quotation, the buyer can ask for documented logic structure, network drawings, alarm lists, cybersecurity assumptions, backup procedures, and lifecycle support expectations.
A controls and automation review matrix
One useful tool for any automation project is a review matrix that compares technical choices with operational consequences. The matrix below can be adapted for new equipment purchases, retrofit projects, or supplier evaluations.
| Review area | Why it matters | Evidence to request |
|---|---|---|
| Control reliability | Determines whether the machine can run safely during network or supervisory failures | Control narrative, failure mode behavior, watchdog strategy, local/manual mode description |
| Maintainability | Affects troubleshooting time and dependence on vendor support | Program structure, tag naming standard, drawings, spare parts list, backup and restore procedure |
| Cybersecurity | Reduces exposure from remote access, unmanaged devices, and weak segmentation | Network diagram, user roles, access method, patch plan, asset inventory, hardening checklist |
| Safety | Protects people, equipment, and compliance position | Risk assessment, safety function list, validation records, bypass management procedure |
| Data usefulness | Determines whether analytics and reporting can support decisions | Tag list, units, timestamps, context model, historian or MES interface specification |
| Lifecycle support | Controls the long-term cost of ownership | Obsolescence plan, software licenses, vendor support term, firmware policy, training material |
This kind of matrix makes automation decisions less subjective. It also exposes weak proposals early. A low-cost panel may become expensive if it lacks backups, diagnostics, spare parts availability, or secure access management.
Common mistakes to avoid
The first mistake is over-automating a poorly understood process. Automation can make a stable process faster and more repeatable, but it can also make an unstable process fail faster. Process knowledge should guide the control strategy.
The second mistake is treating alarms as a substitute for good control. Too many alarms train operators to ignore them. Alarms should be prioritized, actionable, and connected to a defined response.
The third mistake is connecting equipment for data collection without deciding who owns the data, how it is named, how long it is stored, and how it will be used. Data without context rarely delivers operational value.
The fourth mistake is delaying cybersecurity until after commissioning. By then, network topology, user roles, remote access methods, and device selection may already be fixed. Security should be part of the specification, not an afterthought.
The fifth mistake is ignoring documentation. Drawings, backups, software licenses, passwords, change logs, and calibration records are not administrative extras. They are part of the control system’s reliability.
Frequently asked questions
Is controls and automation the same as industrial automation?
They overlap heavily. Industrial automation is the broader application of technology to monitor and control production or service delivery. Controls and automation usually emphasizes the control system architecture, logic, instrumentation, supervision, and integration that make industrial equipment operate reliably.
Should a plant choose PLC, DCS, or SCADA first?
No. The plant should first define the process, safety functions, required response times, operator needs, data requirements, and maintenance model. PLC, DCS, and SCADA choices should follow those requirements.
Does every machine need cloud connectivity?
No. Some machines benefit from cloud analytics, remote dashboards, or fleet monitoring, but local control should remain safe and reliable without a cloud connection. Connectivity should be justified by a clear operational use case.
What is the most important first step in an automation retrofit?
The first step is an accurate asset and risk baseline. Without knowing the installed controllers, I/O, drives, networks, software versions, safety functions, and failure modes, a retrofit plan is likely to miss hidden dependencies.
How can buyers compare automation suppliers fairly?
Ask each supplier for the same evidence: control narrative, architecture diagram, cybersecurity assumptions, safety documentation, alarm approach, backup procedure, data interface specification, spare parts plan, and lifecycle support terms. This makes the comparison more objective than price alone.